Verify your security. Validate your suppliers. Simplify compliance.
Are you doing everything to mitigate cyber risk? Grawlr replays real botnet attack patterns against your sites, shows what got through, and checks the partners your business depends on.
- Free quick scan, no sign-up needed
- No plugins or agents on your server
- Real botnet attack patterns, continuously updated
- Supplier questionnaires for GDPR, NIS2, DORA, EU CRA
- 14-day trial, no commitment
Results in seconds. No credit card required.
Used and trusted by NGOs, online stores, and SaaS companies with annual revenue from €100K to €100M
What happens if you aren't prepared?
Attacks are automated and never stop. A check from last year says little about the site you run today.
600M+
Cyber attacks attempted every day worldwide
Source: Microsoft Digital Defense Report 2024
$4.44M
Average cost of a data breach
Source: IBM Cost of a Data Breach Report 2025
The bill arrives after the attack: downtime, lost customers, incident response, and questions from regulators and partners.
Validate your site against botnet attacks
Does your site hold up against attacks that never stop?
Botnets test every site on the internet, every day. Grawlr runs the same attacks first, on your terms, and shows you what to fix.
- WordPress
- Joomla
- Drupal
- Wix
- Squarespace
- Webflow
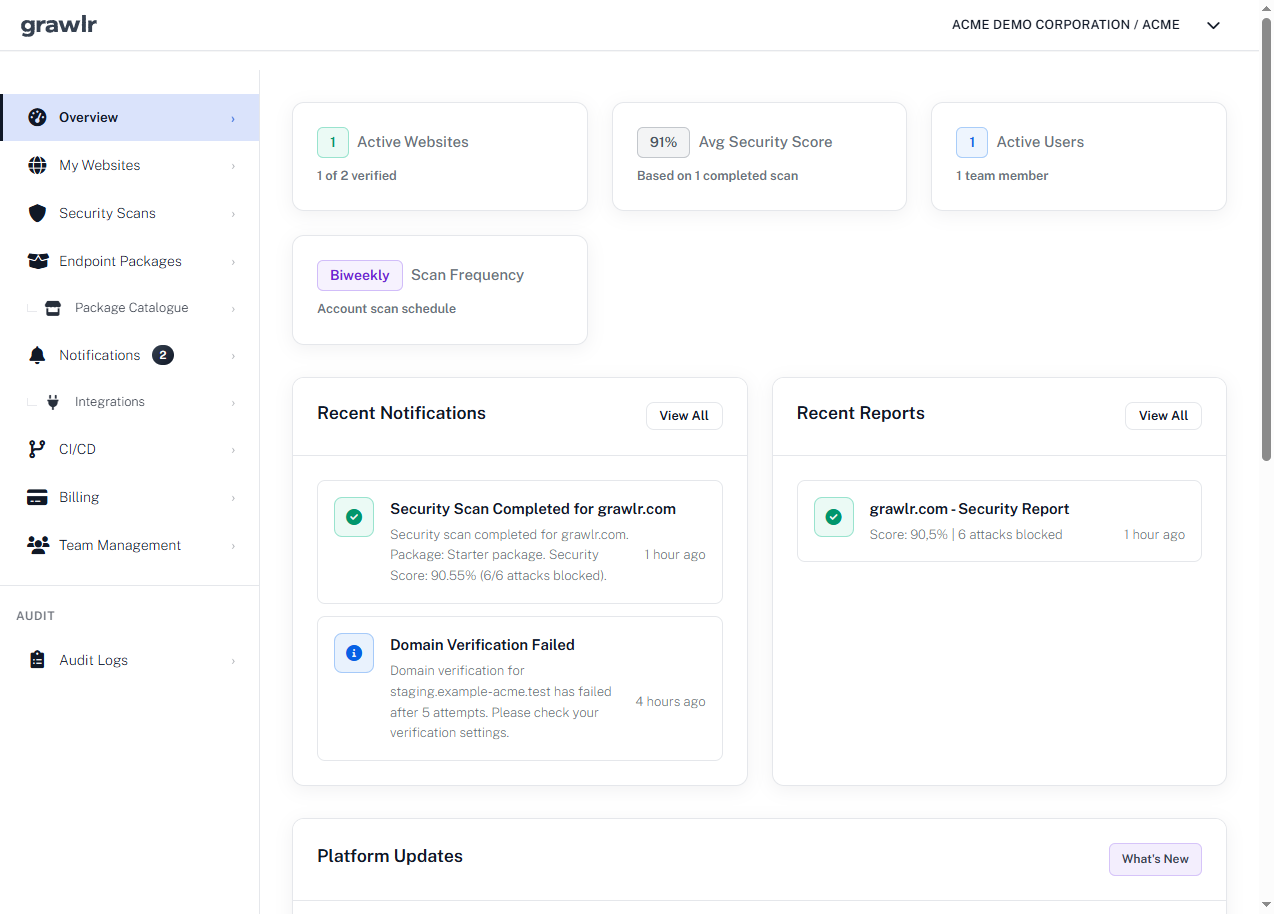
See your exposure at a glance
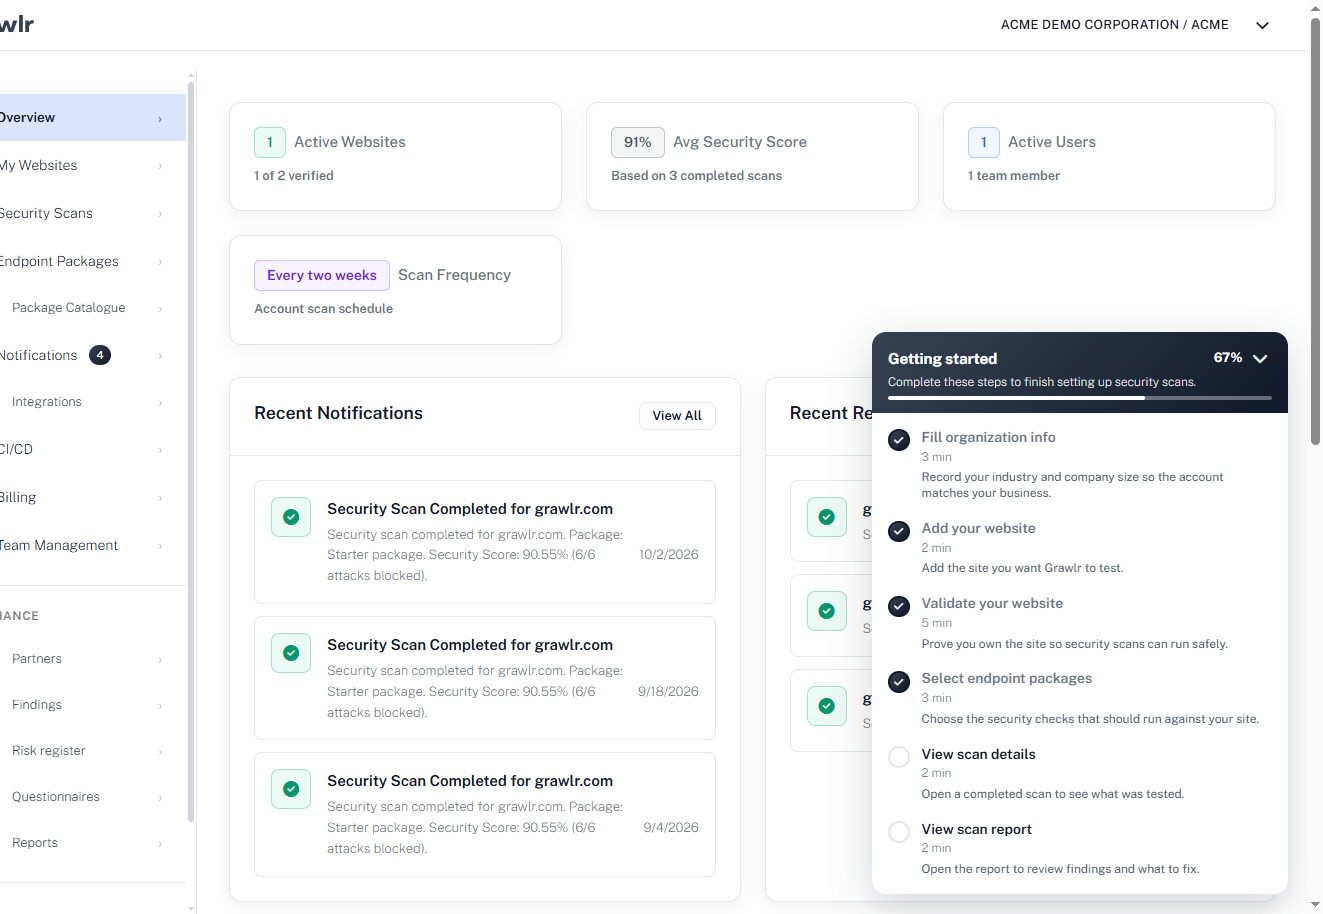
One overview shows how many sites are verified, your average security score, and what the latest scans found—no digging through logs.
Website risk is rarely one big hack. Stolen logins, outdated plugins, exposed admin areas, and untested backups are the weak spots attackers try first.
Scans run on the schedule you set, with no plugins or agents on your server.
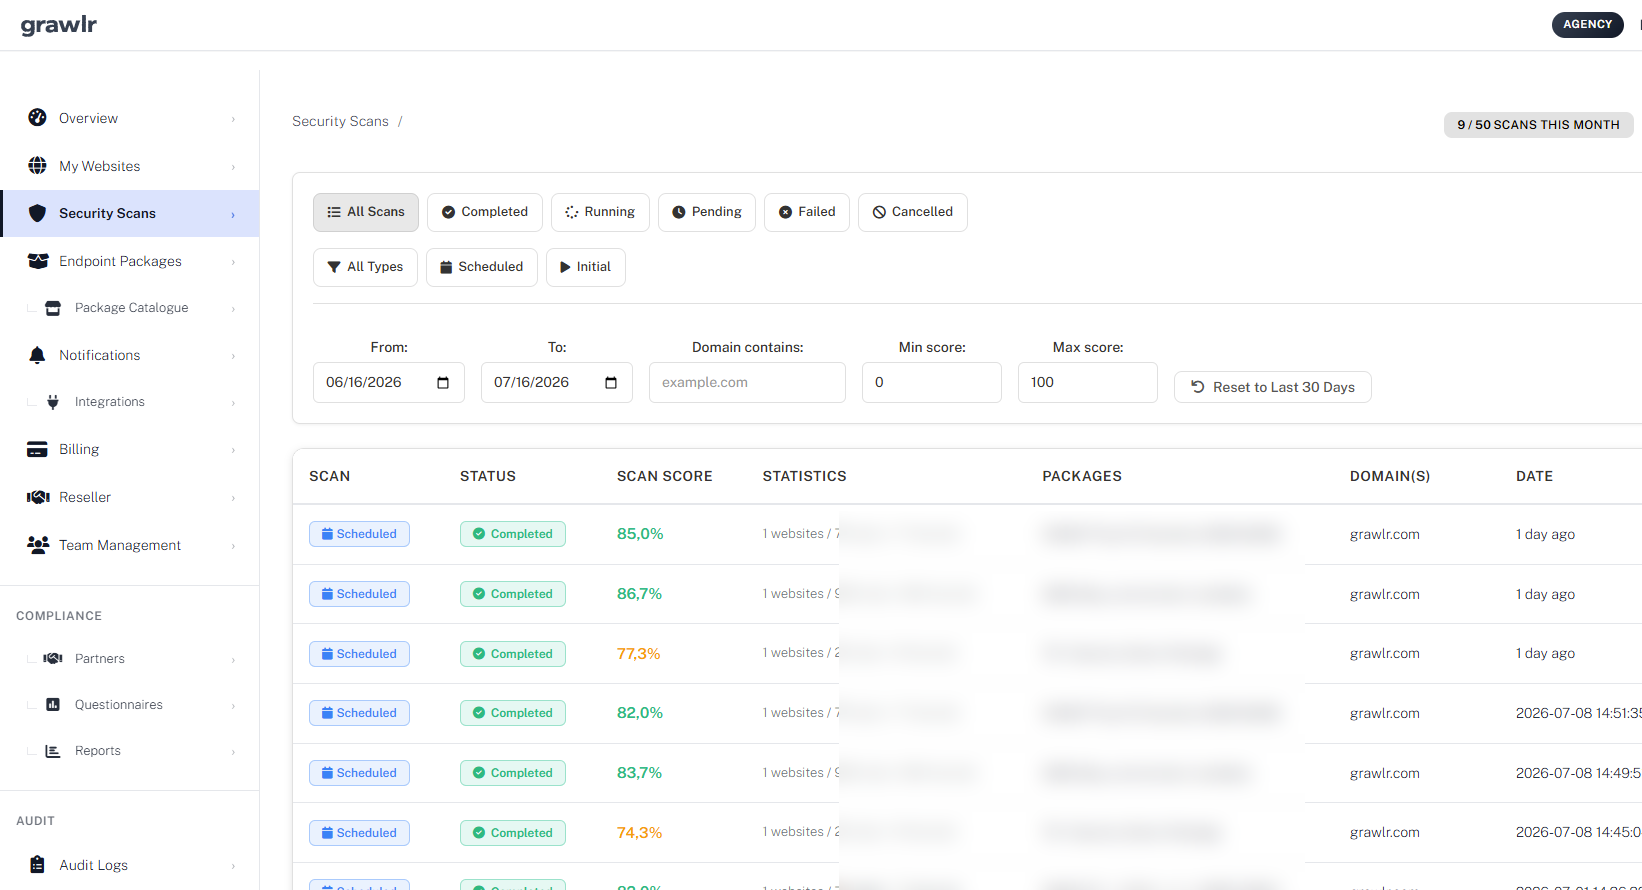
Replay real attack patterns, not checkbox audits
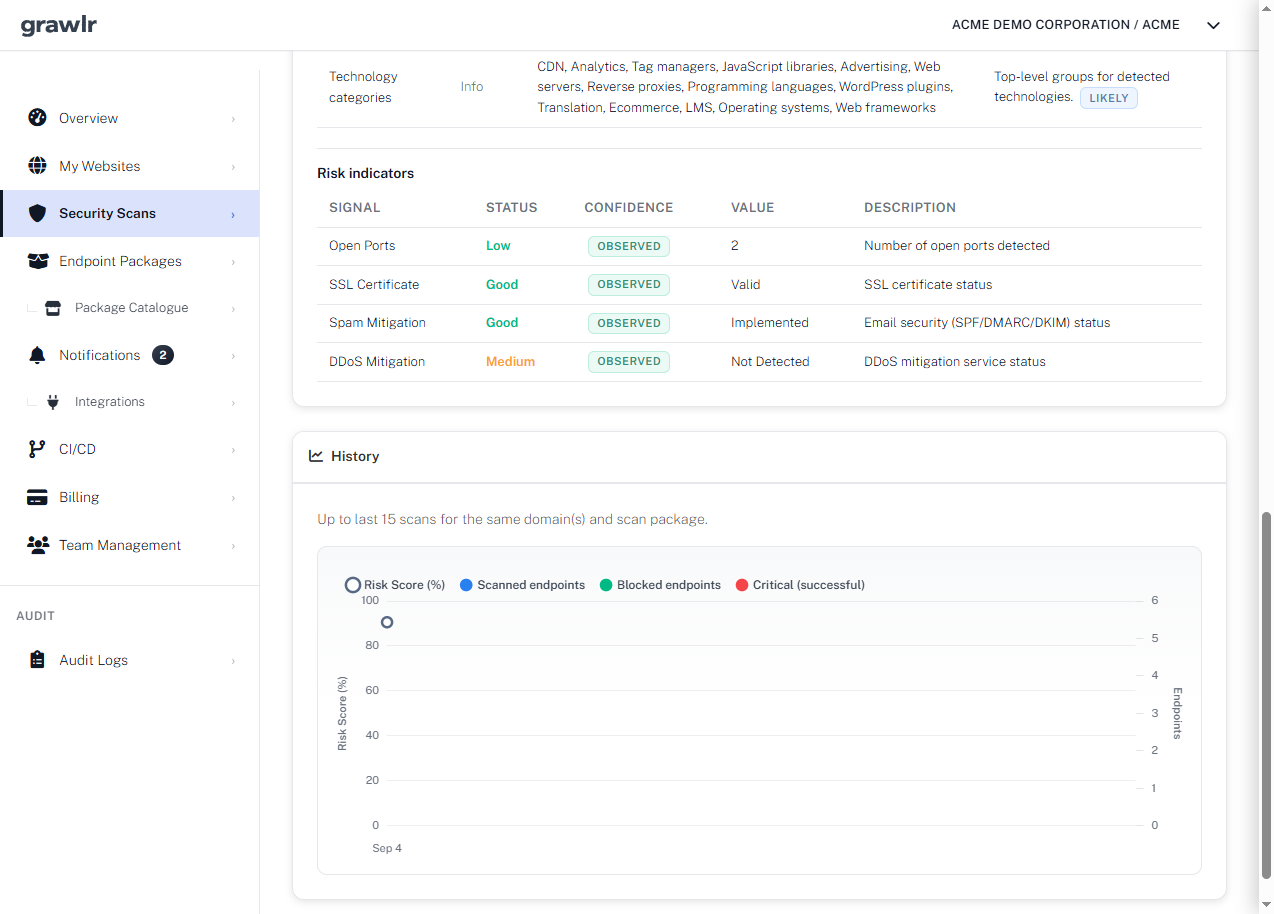
Every scan sends the probes attackers actually use against your endpoints and scores the result, so you can see whether things got better or worse since last time.
Hostile bots retry endlessly and ignore office hours. Even failed attempts cost server capacity and staff time, and can get your site blocked by partners.
Each scan produces a PDF report you can share with your developer or host.
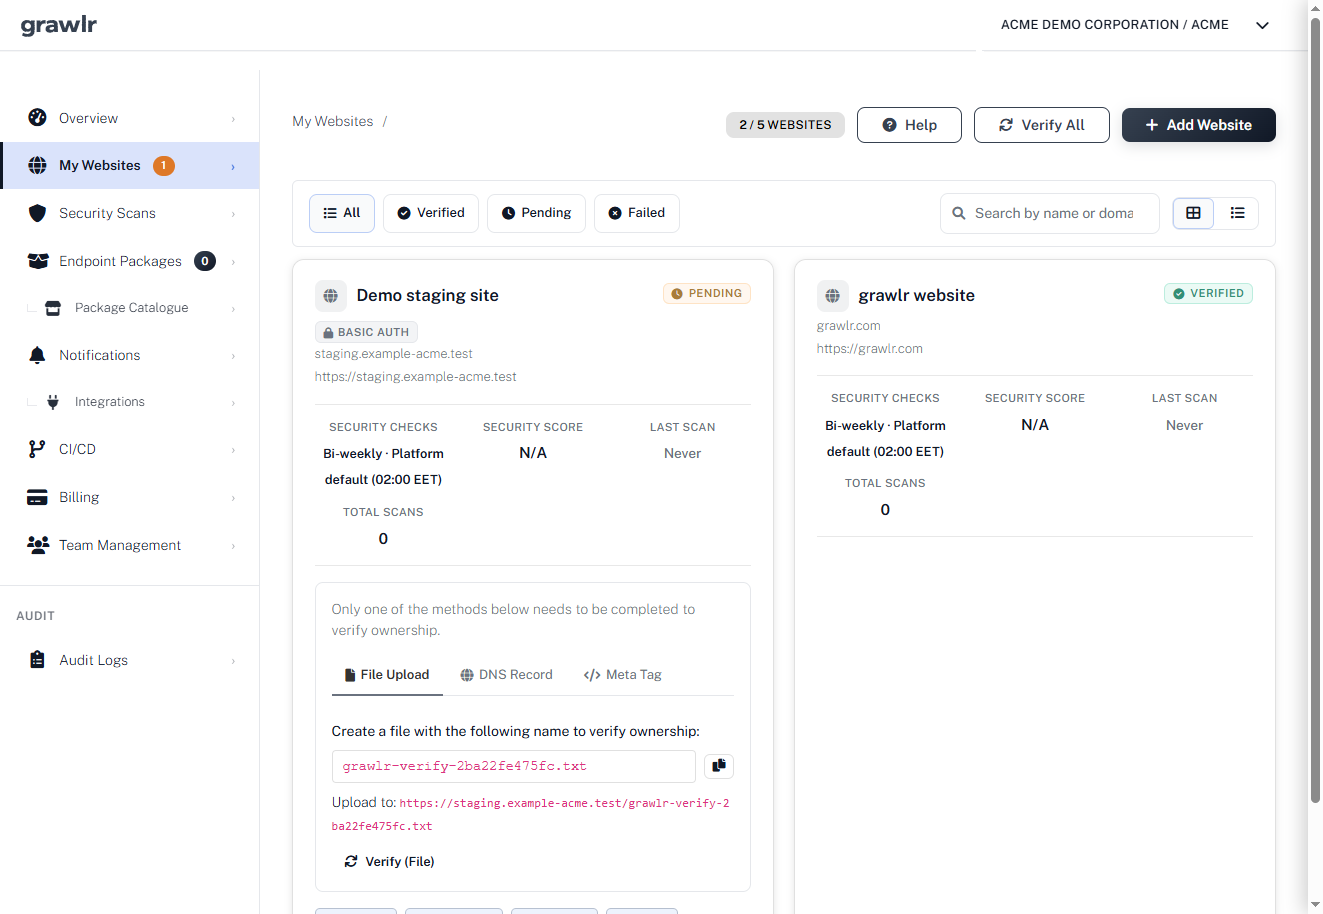
Verify a domain and start in minutes
Add your domain, prove you own it, pick a schedule. Grawlr takes it from there and tells you when something changes.
A check from last year does not describe this week's site. Every new theme, plugin, or snippet changes what attackers can reach.
Not ready to sign up? Run a free quick scan first.
- Shopify
- WooCommerce
- PrestaShop
- Magento
- Shopware
- BigCommerce
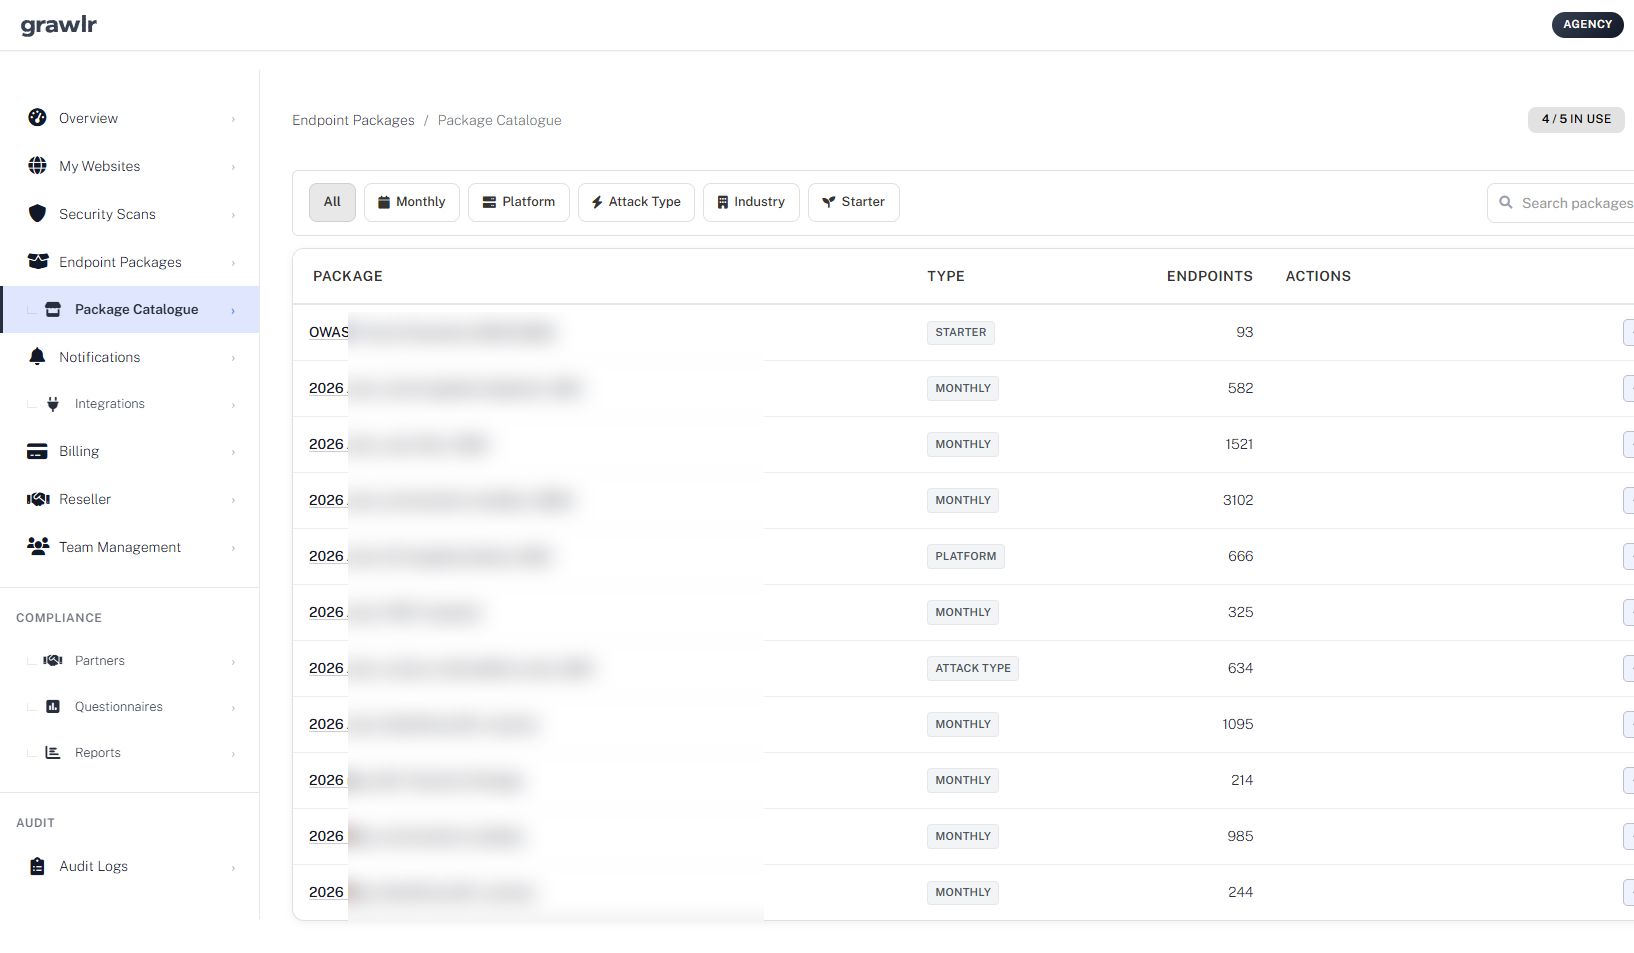
Test the paths bots and fraud tools hit
Pick endpoint packages for your platform—checkout, login, APIs, and plugins—and Grawlr keeps them under test as new attack patterns appear.
Card-testing bots can make your payment provider throttle transactions, so real customers see declines too.
Browse packages by platform, attack type, or industry.
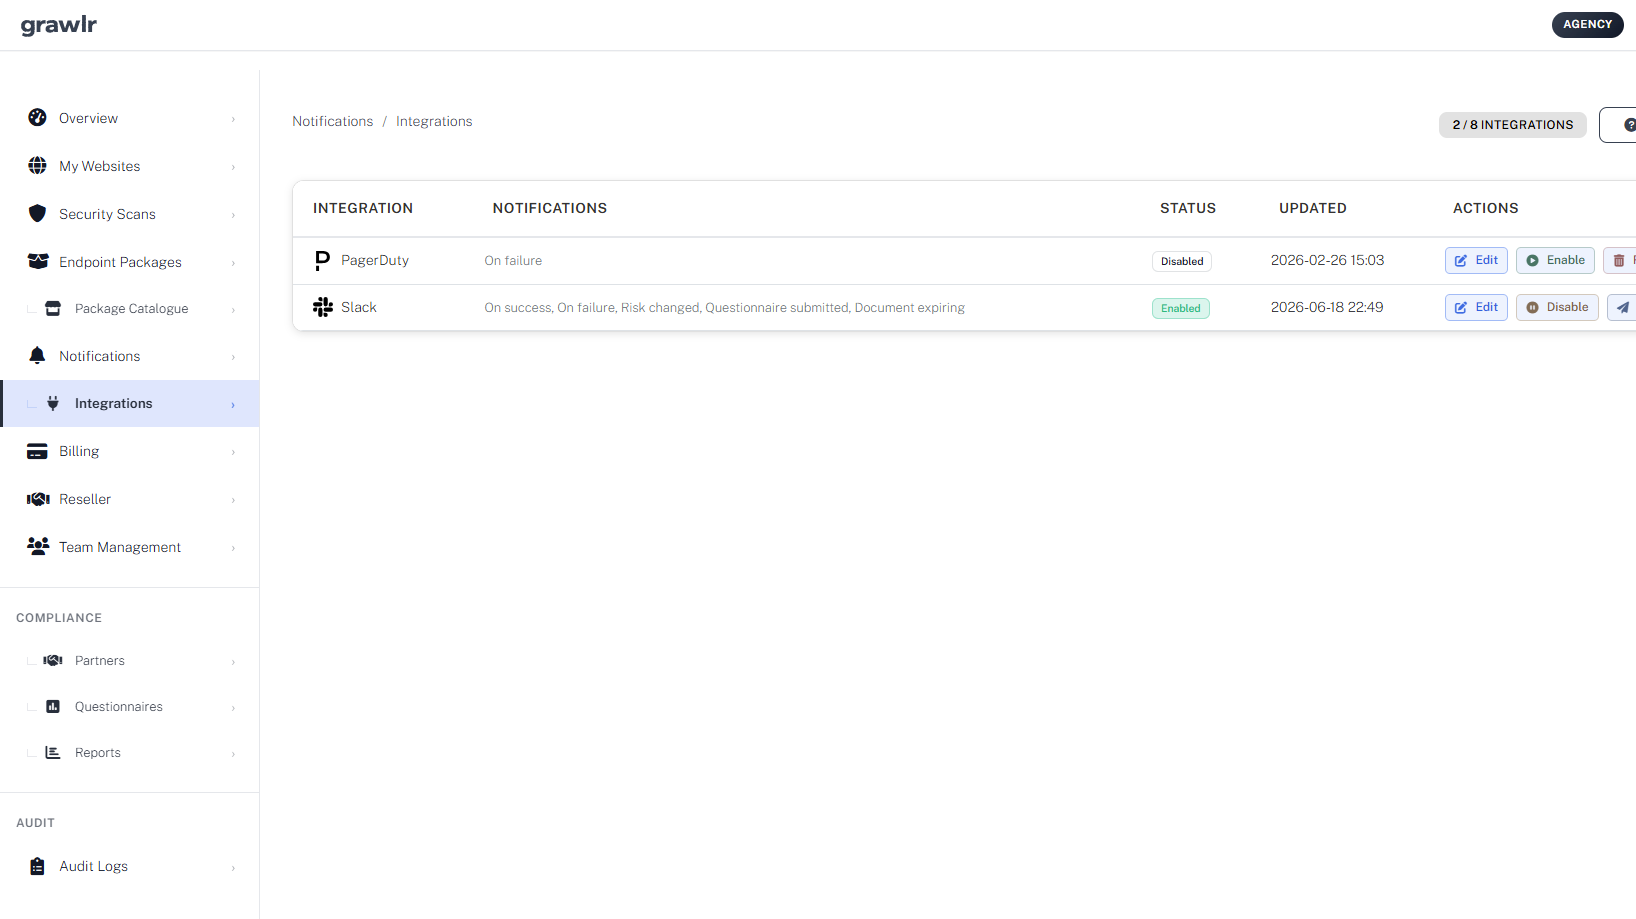
Alert the right person when a test fails
Send failures and risk changes to Slack, Discord, PagerDuty, Opsgenie, Zendesk, or Zapier, so problems reach whoever can fix them before customers notice.
Attackers replay passwords leaked from other sites. A spike in failed logins is often the first warning sign.
Choose which events notify: failures, risk changes, or every result.
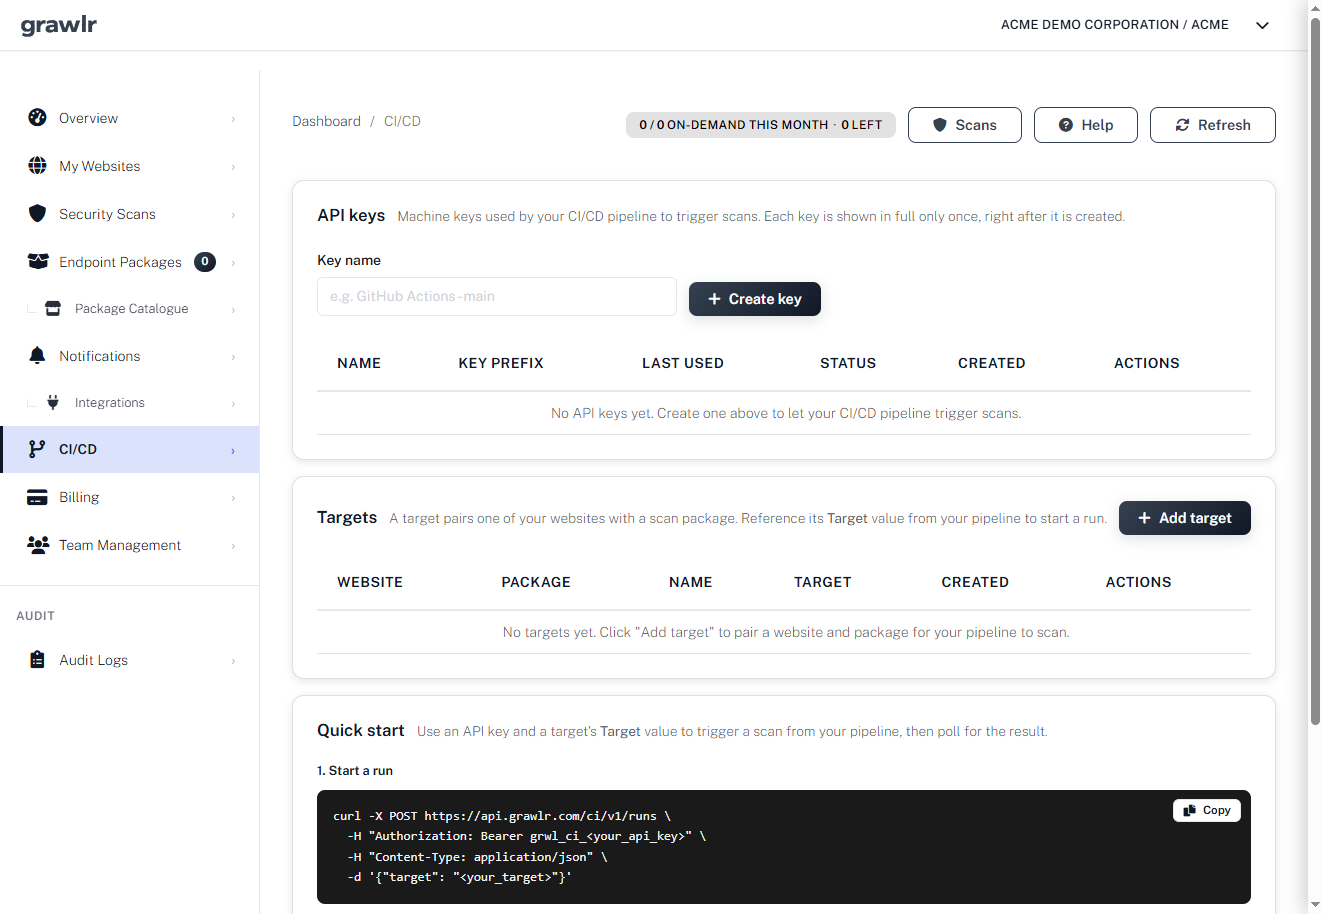
Re-check after every theme or plugin update
Your stack changes weekly. Run an on-demand scan after each release, or trigger one from your deploy pipeline, and compare scores side by side.
An add-on that stops getting updates, or a script compromised at the source, can turn a routine update into a weak link.
Trigger scans from GitHub Actions or any CI/CD pipeline with an API key.
- WordPress
- Shopify
- Laravel
- Spring Boot
- .NET
- React
- Angular
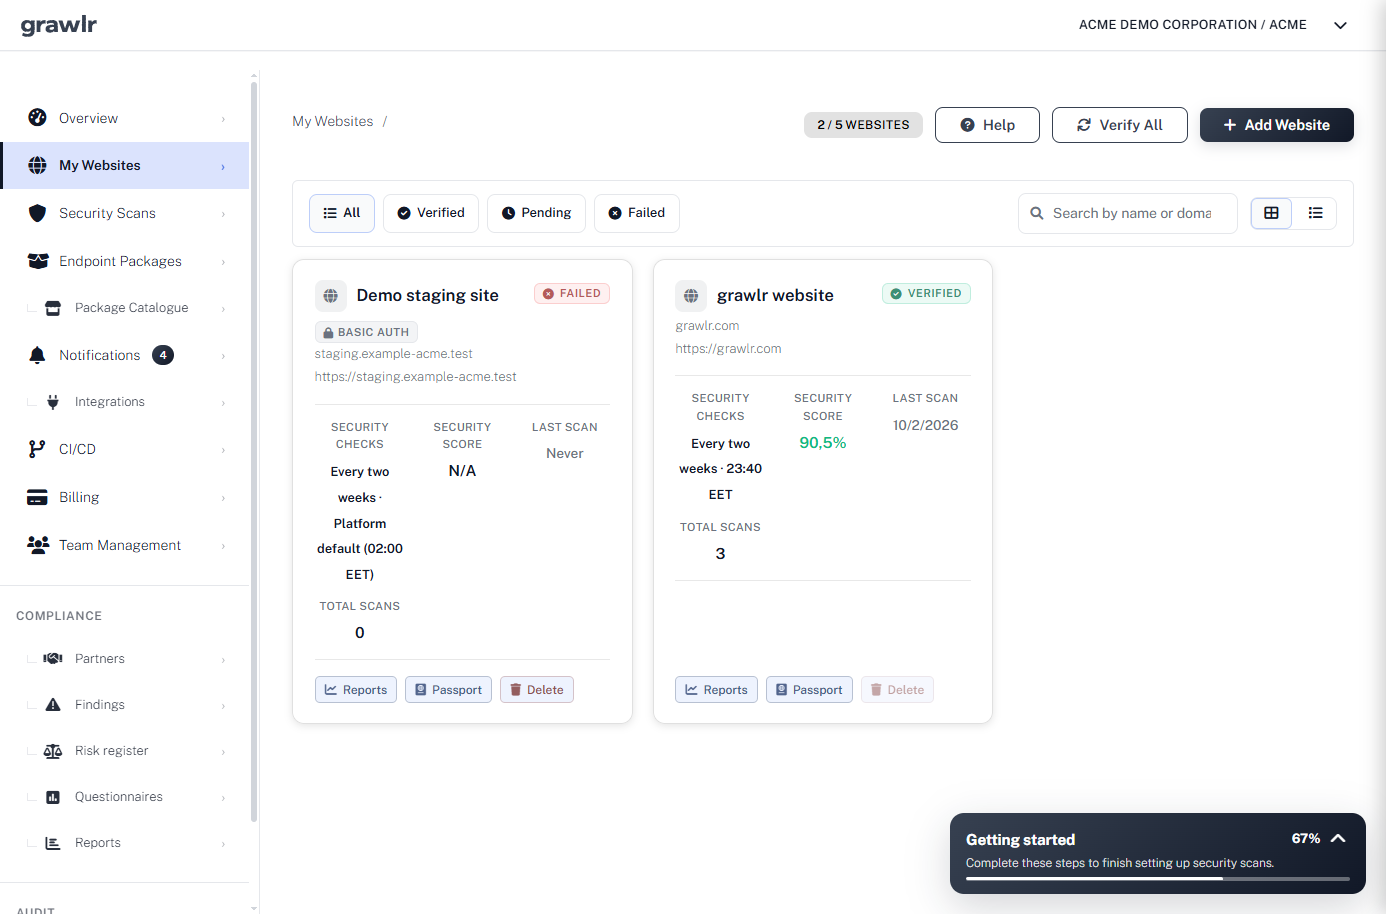
Run security for all your clients from one account
Add client websites to your Agency account and scan every one of them daily. With the reseller program, each client can get their own account under yours.
Your clients may think they are too small to be noticed. Automated attacks notice everyone, and that is why ongoing checks are worth paying for.
The Agency plan covers up to 10 websites with daily scans. Need more sites, scans, or custom tests for cloud apps and frameworks? We can always put together a custom package.
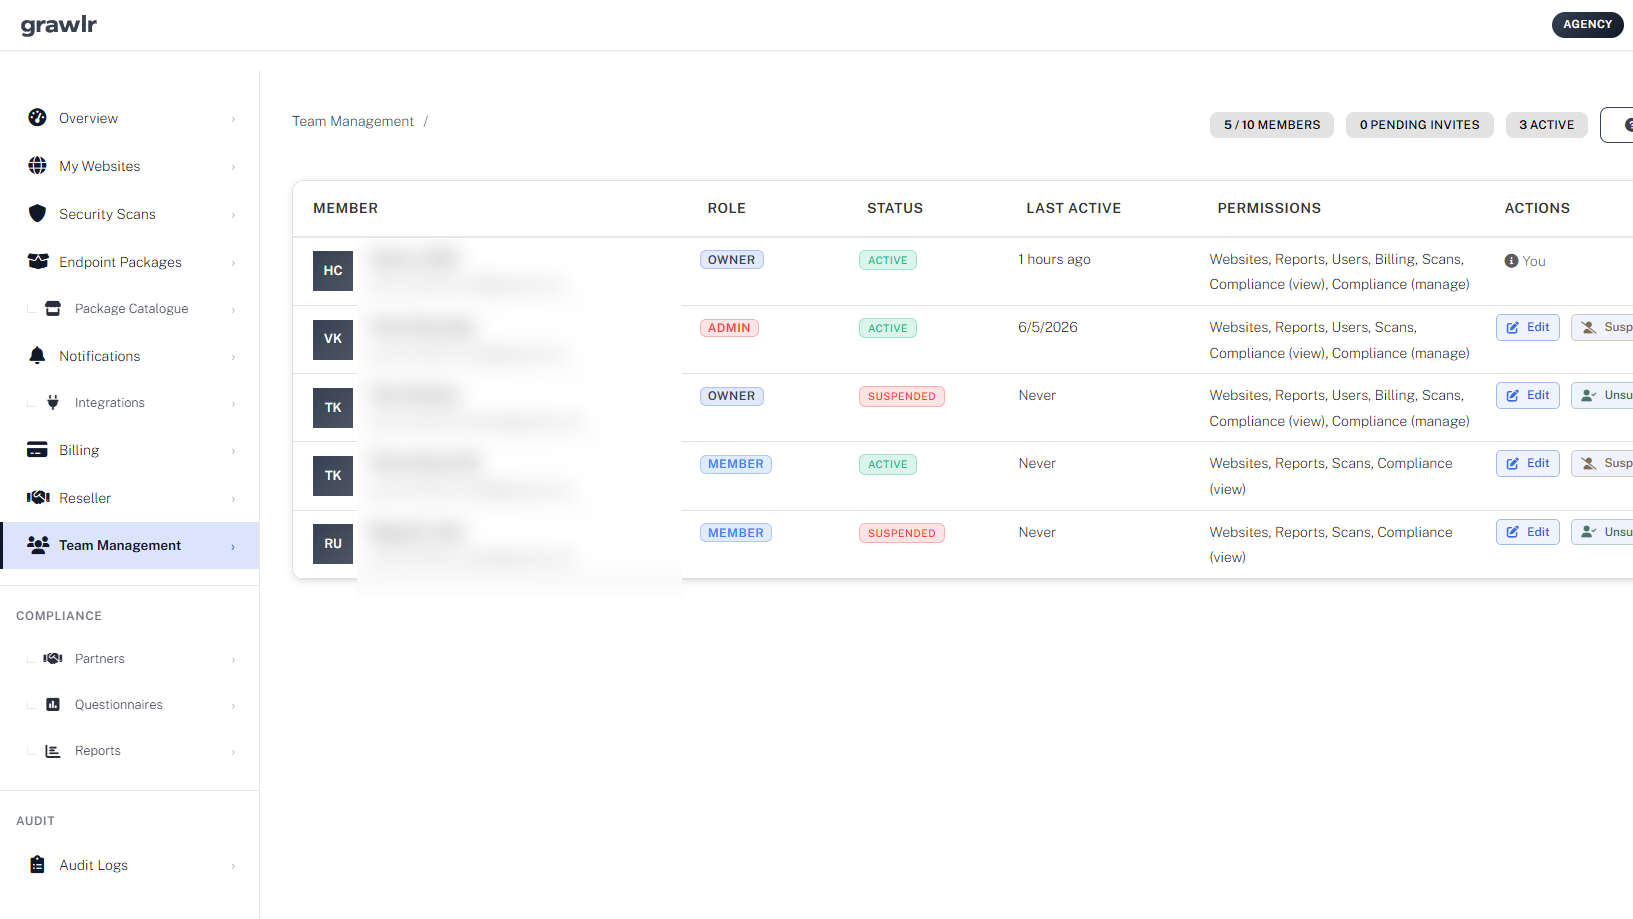
Bring in your team and your clients
Invite up to 15 colleagues and client contacts, each with the right role and permissions for websites, reports, and billing.
A contractor who keeps access after a project ends is a common way in. Limit admin rights and remove people who leave.
Suspend or change access in one click when a project ends.
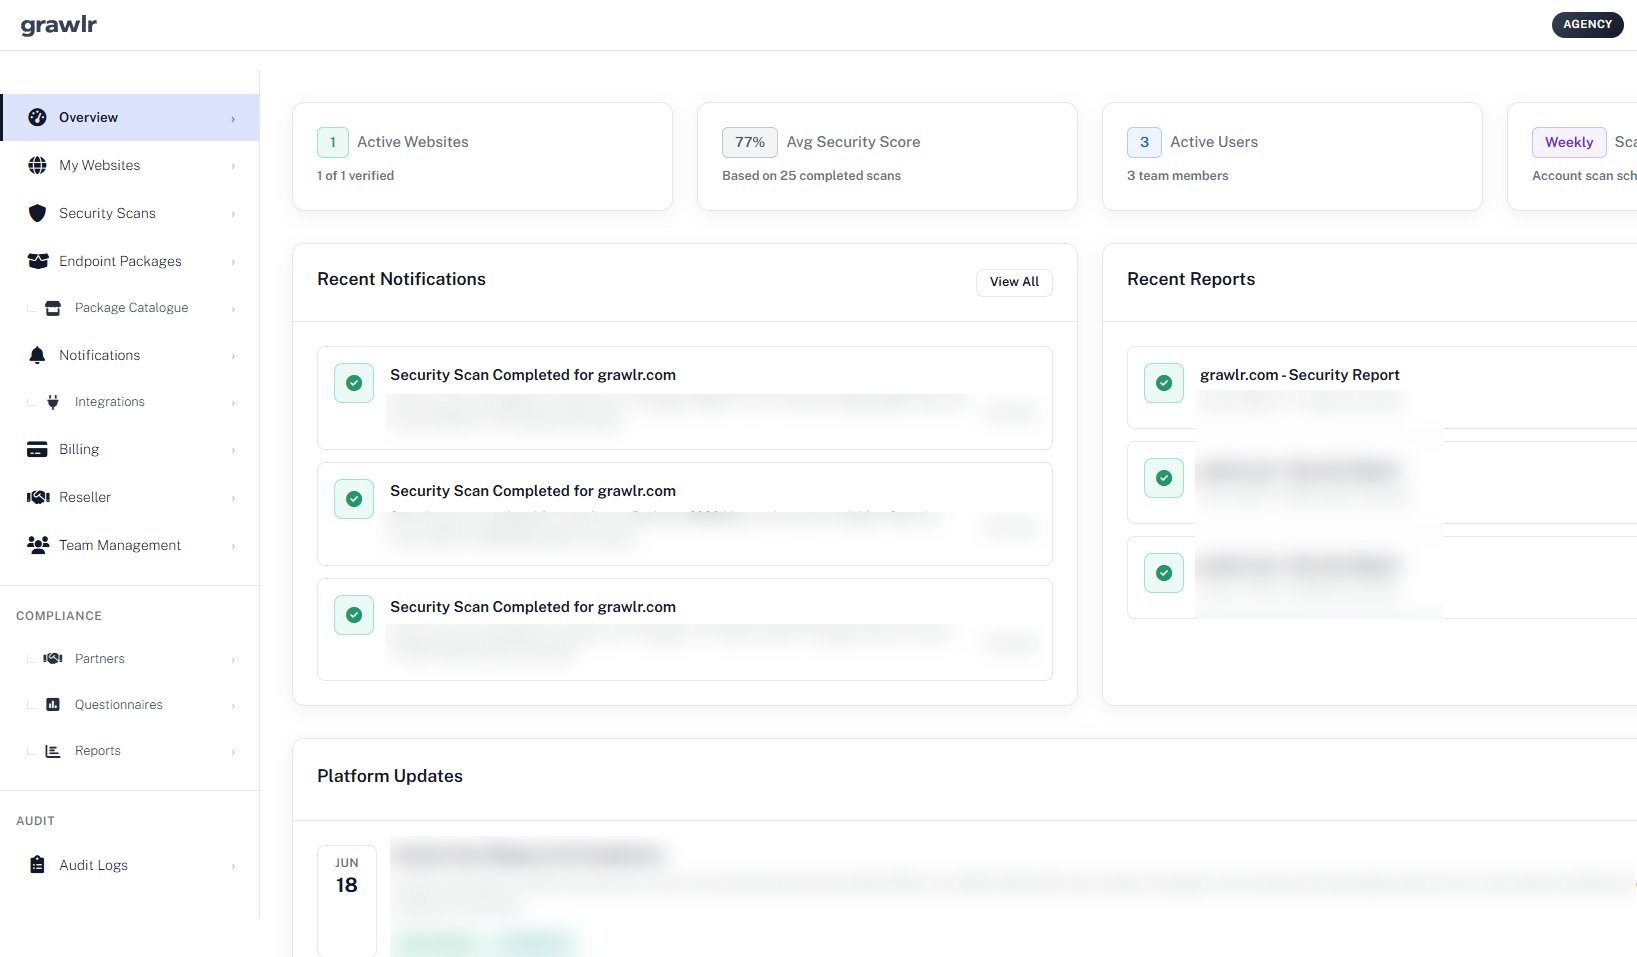
Turn scan results into a service clients pay for
Send clients comprehensive reports on what was tested, what was blocked, and what changed, and package it as a monthly security service.
A useful check ends with a report people can read: what was blocked, what was not, and what changed since last time.
Taking on more clients? The Partner Program adds room for more clients, brandable reports, custom invoicing, and revenue share.
How Grawlr works
Four steps from sign-up to a safer site. After that, it keeps running on its own.
-
Add your sites
Add your websites and confirm you own them. No plugins or agents needed.
-
Test like an attacker
Grawlr replays real attack patterns against your sites on the schedule you choose.
-
Get alerted
Clear reports and alerts show what got through and what changed since last time.
-
Fix and re-check
Close the gaps, scan again, and keep the loop running as your site changes.
Find out what a botnet sees when it looks at your site.
Free. Results in seconds.
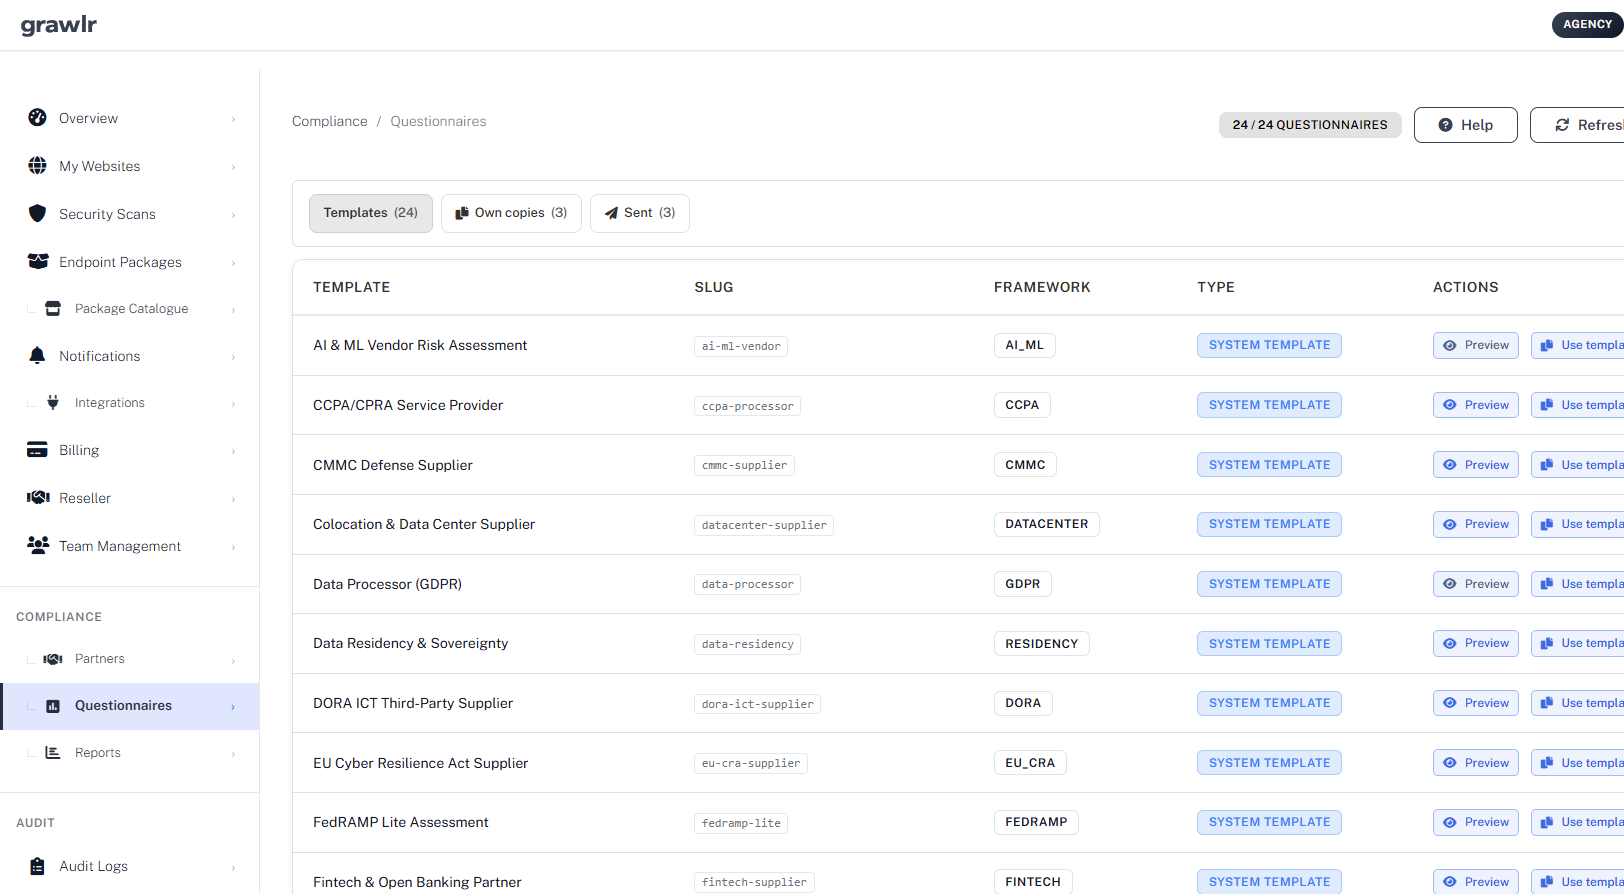
Partner monitoring & compliance
What happens if your business partner gets exploited, and their systems are integrated with yours?
51%
of organizations have had a data breach caused by a third party. Source: Ponemon Institute
- Send ready-made questionnaires. Pick a template for GDPR, NIS2, DORA, the EU Cyber Resilience Act and more, and send it to a supplier in a few clicks.
- Check claims against live scans. Compare what a partner says about their security with what Grawlr actually observes on their public systems.
- Stay audit-ready. Answers, evidence, and changes are kept in one place with an audit trail, ready for your next review.
Included from the Agency plan.
Everything in one platform
From the first scan to the next audit, the tools work together.
Scans that behave like real attackers
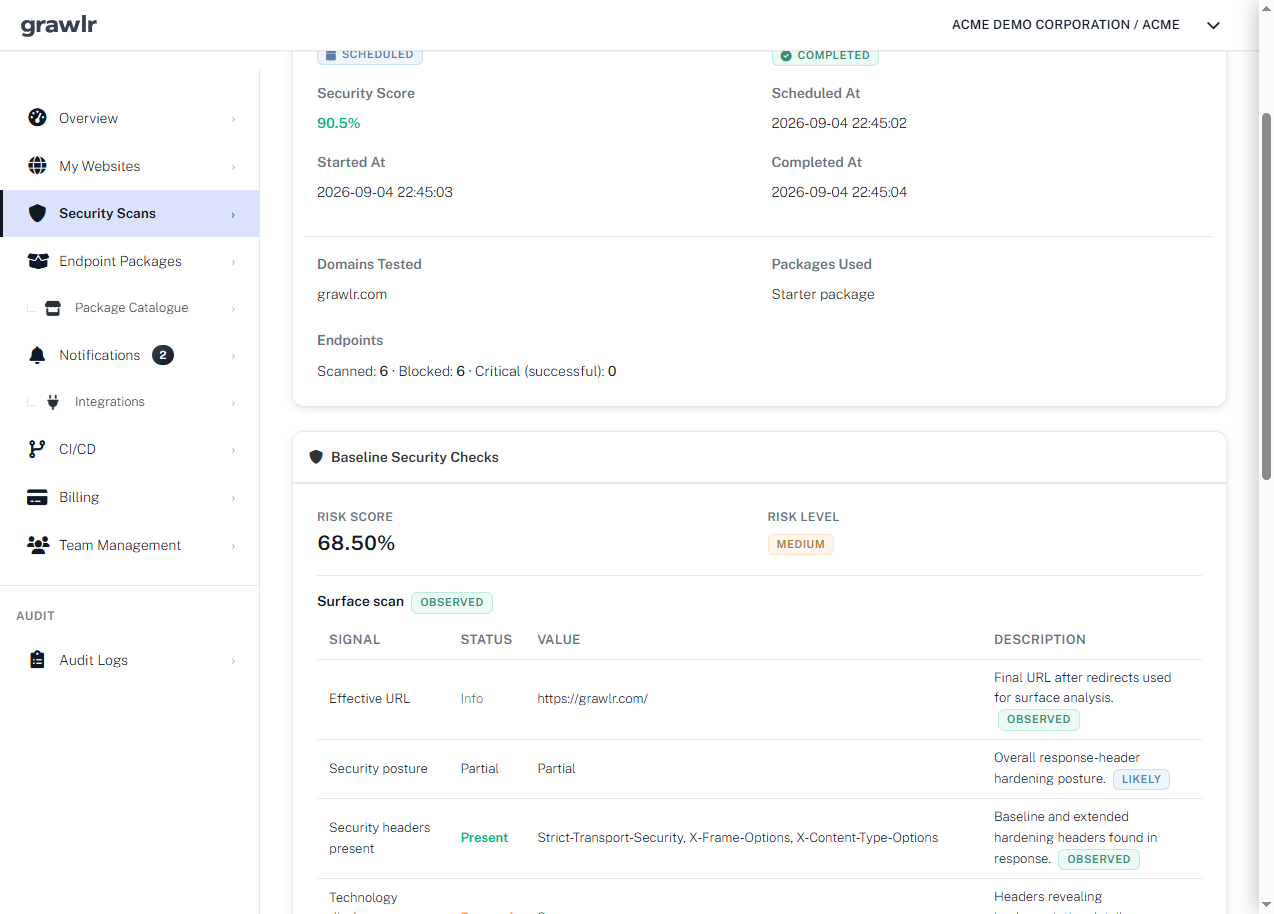
Grawlr replays attack patterns captured from live botnet traffic against your endpoints, then scores what got through.
- Security score and risk level for every run
- Baseline checks for headers, TLS, and exposed technology
- History that shows whether you are improving
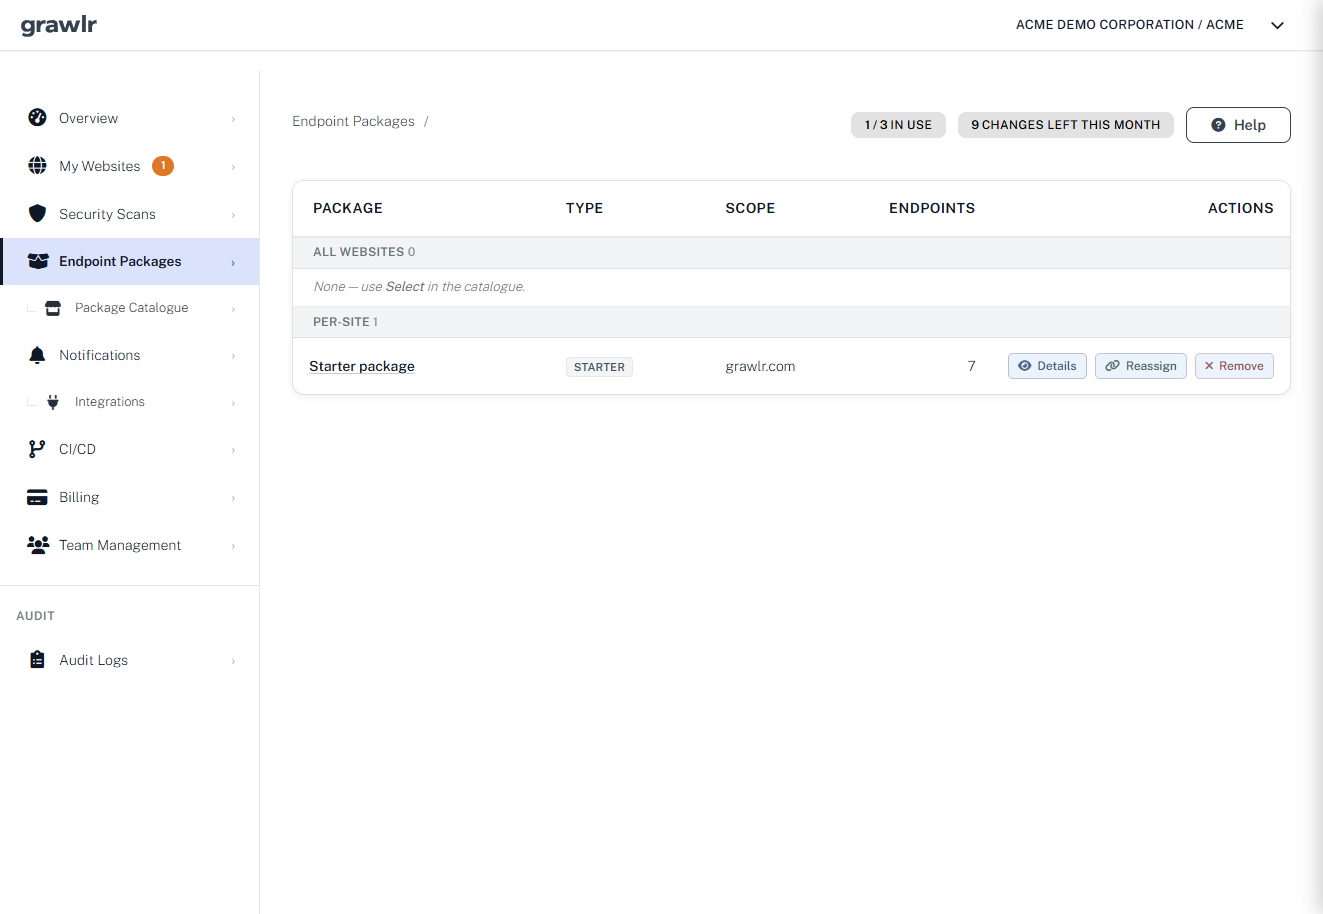
Test the paths that matter for your stack
Choose curated packages for your platform, attack type, or industry and assign them to all websites or just one.
- Packages for CMS, shop, API, and plugin endpoints
- Custom packages for apps on AWS, Azure, or Google Cloud and frameworks like Spring Boot, .NET, React, or Angular
- Assign per site or across the whole account
- New patterns added as attackers change tactics
Problems reach the person who can fix them
Send scan failures, risk changes, and questionnaire events to the tools your team already watches.
- Slack, Discord, Opsgenie, Datadog, Zendesk, n8n, Zapier, and more
- Pick events: failures, risk changes, or every result
- Trigger scans from your CI/CD pipeline
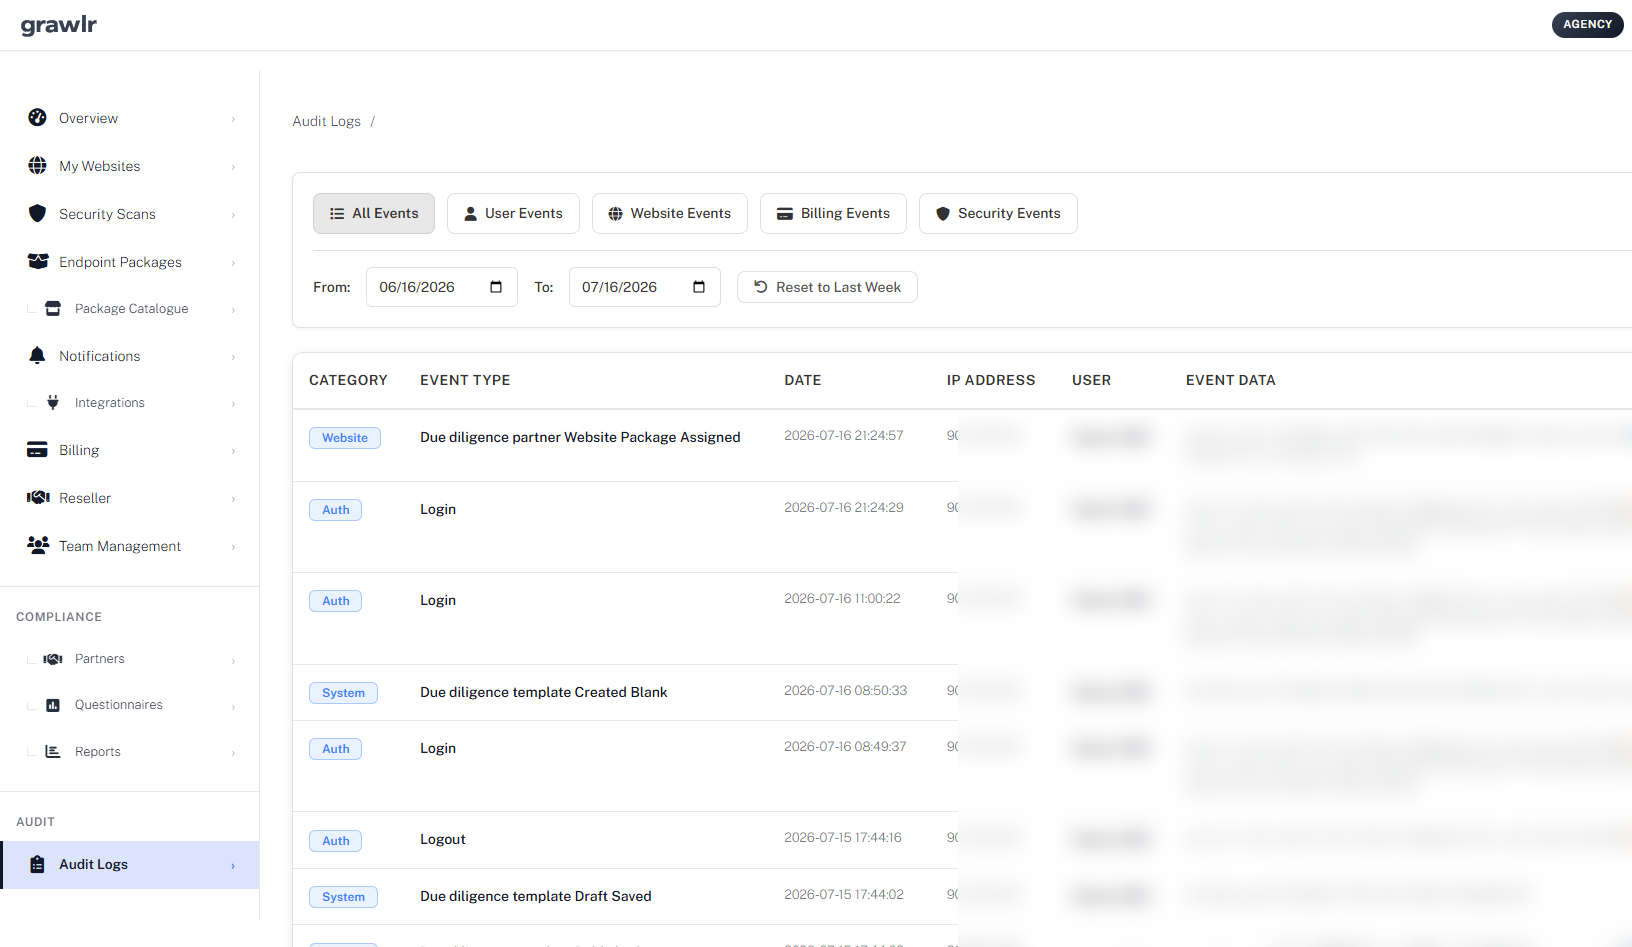
Evidence you can hand to an auditor
Every scan ends in a readable report, and every meaningful account action is recorded in the audit log.
- PDF reports to share with developers, hosts, or clients
- Audit log filtered by user, website, billing, or security events
- Trends over time instead of one-off snapshots
Know which partners put you at risk
Track the suppliers you depend on, send questionnaires, and compare their answers with what scans observe.
- Ready-made templates for major frameworks
- Partner records with scan authorization
- Claims checked against live evidence
Comparison
Is it for me? See how continuous attack testing compares with scanners, firewalls, and one-off penetration tests.
| Security Approach | Traditional Scanners (Qualys, Nessus) |
Web App Firewalls (Cloudflare, AWS WAF) |
Penetration Testing (Manual Services) |
Grawlr (Continuous attack testing) |
|---|---|---|---|---|
| Attack validation | ||||
| Detection Method | Static signatures only | Known pattern blocking | Manual testing only | Learns from real attack behavior |
| Attack Intelligence | Generic vulnerability database | Rule-based protection | One-time assessment | Live botnet attack patterns |
| Testing Frequency | Monthly at best | No testing (blocking only) | Quarterly or yearly | Automated recurring scans |
| Setup Complexity | Complex deployment | DNS changes required | Weeks of scheduling | 5-minute domain verification |
| Partner monitoring & compliance | ||||
| Supplier Claim Validation | No supplier questionnaires | Not applicable | Point-in-time questionnaires at best | Claims checked against live scan evidence |
| Vendor Risk Questionnaires | No built-in vendor risk module | Not applicable | Usually a separate consulting engagement | Questionnaires, partner tracking, and risk scoring in one place |
| Compliance Reporting | Findings export, limited business context | No compliance evidence reports | Manual PDF reports per engagement | Comparison and trend reports for audits and vendor reviews |
| Cost | ||||
| Cost Structure | Typically hundreds to thousands per month | Usage-based protection pricing | Thousands per engagement | From €8.99 per month |
Frequently asked questions
Can I run attack tests on my live site?
You can, but treat it like a real attack. Grawlr only tests domains you have verified, runs the packages you choose, and avoids destructive exploitation. Heavier packages still send real attack traffic, which can slow down or even take down a fragile site. We strongly recommend testing a staging or test environment first, keeping a current backup, and scheduling production scans outside peak hours. Staging sites behind HTTP Basic Auth are supported.
Do I need to install anything?
No. Scanning needs no agent, plugin, or changes to your server. The only setup step is a one-time ownership check: upload a file, add a DNS record, or add a meta tag. After that, Grawlr tests your site from the outside like an attacker would.
How is this different from a firewall?
A firewall blocks traffic it recognizes. Grawlr checks whether your defenses actually hold by replaying real botnet attack patterns against your site and showing what got through. The two work well together.
How do supplier questionnaires work?
Pick a ready-made template, send it to a supplier, and they answer through a secure link without needing an account. Their answers sit next to what Grawlr observes on their public systems, so you can spot claims that do not match.
Which frameworks are covered?
Templates include GDPR, NIS2, DORA, the EU Cyber Resilience Act, ISO 27001, SOC 2, PCI DSS, HIPAA and more. They help you collect evidence from suppliers; they are not a certification of Grawlr or of your business.
What does the free quick scan include?
A snapshot of how exposed your site looks from the outside, ready in seconds: how you compare with your industry, whether basic browser protections are set, and what software details your site gives away. No sign-up and no credit card. For full attack testing, start a trial.
More questions? Read the full FAQ
Find your weak spots before attackers do
Run a free quick scanFree quick scan. No credit card required.